

Last Updated on: 17th May 2026, 03:08 pm
Table of Contents
- What is an SSL certificate?
- How SSL certificates build trust and protect your site
- SSL certificate types and real-world adoption
- Common pitfalls and best practices for SSL certificate management
- Getting started: Steps to secure your website with SSL
- Why most website owners overcomplicate SSL — what really matters
- Secure your website with confidence
- Frequently asked questions
Key Takeaways
| Point | Details |
|---|---|
| SSL is essential | Every website needs SSL to protect visitors and gain their trust. |
| DV certificates dominate | Most websites use Domain Validated (DV) SSL because it’s fast, free, and secure enough for most needs. |
| Automate renewal | Use tools or hosting services to automate SSL setup and renewal for continuous protection. |
| No performance worries | Modern SSL adds minimal overhead and can actually boost your site’s SEO and user confidence. |
What is an SSL certificate?
SSL stands for Secure Sockets Layer. It’s the technology that creates an encrypted connection between a web server and a visitor’s browser. In practice, most modern websites use TLS (Transport Layer Security), which is the updated and more secure version of SSL. The two terms are often used interchangeably, so don’t be confused when you see “TLS” mentioned alongside “SSL.”
When a visitor lands on your site, an SSL certificate does two important things. First, it encrypts the data traveling between your server and their browser, so no one can intercept and read it. Second, it verifies that your website is actually who it claims to be, not an imposter site trying to steal information.
Here’s what an SSL certificate actually contains:
- Your domain name (for example, yourwebsite.com)
- The name of the certificate authority (CA) that issued it
- The certificate’s expiration date
- A public encryption key used to establish the secure connection
- A digital signature that proves the certificate is legitimate
When a browser connects to your site, it checks all of these details in a fraction of a second. If everything checks out, the connection is marked as secure and the padlock icon appears in the address bar. If something is off, the browser shows a warning that sends most visitors running.
“An SSL certificate is not just a technical formality. It’s the handshake that tells your visitors their data is safe with you.”
The scale of SSL adoption makes this even clearer. 10.94 billion certificates were issued in Q1 2026 alone, illustrating just how widespread and expected SSL has become across the web. This is not a niche security measure anymore. It’s the standard.
Understanding this foundation helps you see SSL not as a technical burden but as a basic feature your website needs to function properly in the modern web environment.
How SSL certificates build trust and protect your site
Now that you understand the basics, let’s explore why SSL is considered essential for any modern website and the importance of ssl certificates in protecting both businesses and visitors.
The most obvious benefit is security. Without SSL, any data your visitors submit through your website, whether that’s a contact form, a login, or a newsletter signup, travels across the internet as plain text. Anyone positioned between your server and the visitor’s browser can read it. This kind of attack is called a “man-in-the-middle” attack, and it’s more common than most people think. SSL encryption makes that intercepted data unreadable.
Beyond raw security, SSL builds trust with your visitors in a very visible way. Browsers like Chrome and Firefox actively flag non-HTTPS sites as “Not Secure” in the address bar. That warning appears before a visitor even reads a single word on your page. Studies consistently show that users abandon sites displaying security warnings. If your site isn’t secured with SSL, you’re losing visitors before they even give you a chance.
“A missing padlock icon is the modern equivalent of a broken front door. Visitors notice it immediately, and most will turn around.”
Search engines also factor SSL into rankings. Google has confirmed that HTTPS is a ranking signal, meaning sites with SSL certificates have a modest but real advantage in search results over those without. For small websites competing for visibility, every advantage counts.
Performance is not a concern with modern SSL. This is a common misconception worth addressing directly. Modern stacks (TLS 1.3 + ECDSA) add less than 5% overhead to page load times and can actually optimize your Core Web Vitals scores, which are metrics Google uses to evaluate user experience. In other words, SSL doesn’t slow your site down in any meaningful way. If anything, it supports better performance.
The combination of security, user trust, SEO benefit, and negligible performance cost makes SSL a straightforward decision. There’s no real trade-off here. The only question is which type of certificate you need and how to set it up correctly.
SSL certificate types and real-world adoption
Understanding the value of SSL, it’s important to know the different types available and what’s actually popular in real-world websites.
There are three main categories of SSL certificates, each offering a different level of identity verification.
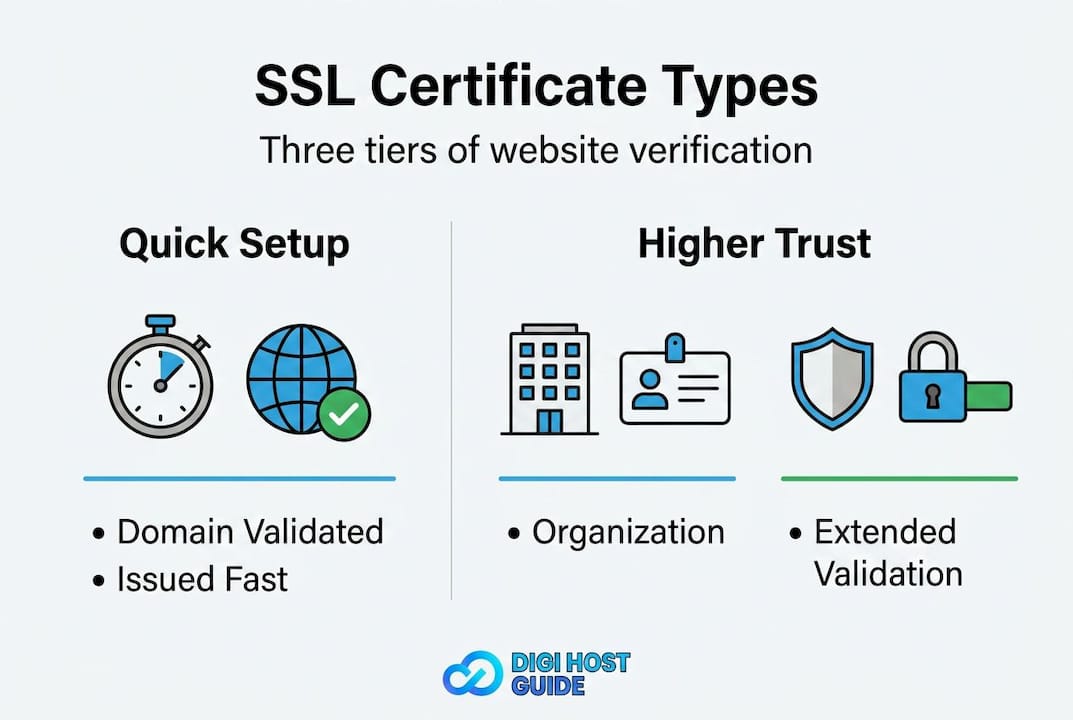
| Certificate type | Validation level | Best for | Typical issuance time |
|---|---|---|---|
| Domain Validated (DV) | Domain ownership only | Blogs, small sites, personal projects | Minutes |
| Organization Validated (OV) | Domain + business identity | Business websites, nonprofits | 1 to 3 days |
| Extended Validation (EV) | Full legal entity verification | Banks, large e-commerce, enterprises | 1 to 2 weeks |
Domain Validated (DV) certificates are by far the most common. To get one, you simply prove that you own the domain, usually by clicking a link in an email or adding a small DNS record. The process is fast, often automated, and free through services like Let’s Encrypt.
Organization Validated (OV) certificates require the certificate authority to verify your business exists. This adds a layer of credibility, which can matter for professional service firms or established businesses that want visitors to see verified company details.
Extended Validation (EV) certificates involve the most thorough vetting process. They were once associated with a green address bar in browsers, though most browsers have since removed that visual indicator. EV certificates are now mainly used by large financial institutions and enterprises where regulatory compliance demands them.
The real-world numbers tell a clear story. 96.8% of SSL certificates are Domain Validated, and ECDSA (Elliptic Curve Digital Signature Algorithm) usage is rising fast because it offers strong security with smaller key sizes and faster processing.
Key trends shaping SSL adoption today:
- Short-lived certificates are becoming the norm, with many now set to expire in 90 days or less to reduce risk from compromised keys
- Automation through the ACME protocol (used by Let’s Encrypt) has made certificate management hands-free for most sites
- ECDSA algorithms are replacing older RSA keys because they’re more efficient and equally secure
For most website owners reading this, a DV certificate is all you need. It’s free, fast to set up, and covers everything a blog, portfolio, or small business site requires.
Common pitfalls and best practices for SSL certificate management
Once you’ve chosen the right SSL certificate, maintaining it safely is crucial. Here’s how to avoid the mistakes that trip up most website owners.
The single biggest SSL problem is certificate expiration. When your certificate expires, browsers immediately show a security warning to every visitor. Your site doesn’t go offline, but it effectively becomes inaccessible because almost no one will click past a “Your connection is not private” warning. This is entirely preventable.
Expiration is the most common SSL failure, so the best practice is to automate renewal at least 30 days before the expiration date. Tools like Certbot and cert-manager handle this automatically using the ACME protocol, which is the same system Let’s Encrypt uses.
Here are the best practices every website owner should follow:
- Enable auto-renewal. Set it up once and let it run. Most hosting providers offer this as a built-in feature, and Let’s Encrypt certificates renew automatically when you use Certbot.
- Test your SSL setup before going live. Use free tools like SSL Labs’ SSL Test (ssllabs.com/ssltest) to check your configuration. It grades your setup and flags any weak settings.
- Enable HSTS (HTTP Strict Transport Security). This tells browsers to always use HTTPS when connecting to your site, even if someone types “http://” manually. It prevents a class of attacks that try to downgrade your connection to unencrypted HTTP.
- Enable OCSP stapling. OCSP (Online Certificate Status Protocol) stapling speeds up the verification process by having your server deliver certificate status information directly, rather than making the browser check with the certificate authority separately. It’s a small tweak with a real performance and privacy benefit.
- Watch for mixed content issues. After installing SSL, check that all resources on your pages (images, scripts, stylesheets) load over HTTPS. A single HTTP resource can trigger browser warnings even on an otherwise secured site.
Pro Tip: Set a calendar reminder 45 days before your certificate’s expiration date as a backup, even if you have auto-renewal enabled. If something goes wrong with the automated process, you’ll have time to fix it before visitors are affected.
Staying on top of these basics keeps your SSL setup running smoothly without requiring constant attention.
Getting started: Steps to secure your website with SSL
Now let’s pull everything together with a simple walkthrough so you can secure your website today.
Most certificates are now issued by automation-friendly providers like Let’s Encrypt, making the process straightforward even for beginners. Here’s how to approach it step by step.
Decide which certificate type you need. For most personal sites, blogs, and small business websites, a free DV certificate from Let’s Encrypt is the right choice. If you run a business that handles sensitive customer data and want verified company details in the certificate, consider an OV certificate from a paid provider like DigiCert or Sectigo.
Check your hosting provider first. Many hosting providers, including most shared hosting platforms, include free SSL certificates and install them automatically when you add a domain. Log into your hosting control panel and look for an SSL section. In many cases, you can enable HTTPS with a single click.
Install Certbot if you manage your own server. If you’re on a VPS or dedicated server, Certbot is the standard tool for obtaining and renewing Let’s Encrypt certificates. It integrates with popular web servers like Apache and Nginx and handles the entire process, including renewal.
Set up auto-renewal and confirm it works. After installation, run a test renewal to make sure the automated process functions correctly. Certbot includes a built-in command for this: “certbot renew –dry-run`. This simulates a renewal without actually changing anything, so you can verify the setup is working.
Redirect all HTTP traffic to HTTPS. Once SSL is active, configure your server or hosting panel to redirect any visitor who lands on the HTTP version of your site to the HTTPS version automatically. This is usually a one-line change in your server configuration or a toggle in your hosting control panel.
Check for mixed content. Use your browser’s developer tools or a free online checker to scan your pages for resources still loading over HTTP. Update those URLs to HTTPS or use protocol-relative URLs to fix the issue.
Run a final SSL test. Visit SSL Labs and test your domain. Aim for an A or A+ grade. If you score lower, the report will tell you exactly what to fix.
Pro Tip: After installing SSL, search your website’s database or files for hardcoded “http://” URLs and update them to “https://”. In WordPress, a plugin like Better Search Replace can do this safely across your entire database in minutes.
Following these steps puts you in a strong position from day one, with a secure site, automated maintenance, and a configuration that holds up under scrutiny.
Why most website owners overcomplicate SSL — what really matters
With all the technical details considered, here’s a grounded view based on experience and industry best practices.
There’s a tendency in the web industry to treat SSL as more complicated than it actually is. Forum threads spiral into debates about certificate authorities, key sizes, and validation levels. Most of that complexity simply doesn’t apply to the average website owner.
The truth is that automation and basic monitoring solve 95% of SSL problems before they start. Automating ACME renewal with Certbot or cert-manager, monitoring expiry dates, enabling HSTS, and testing with SSL Labs covers nearly everything you’ll ever need. A DV certificate from Let’s Encrypt, properly configured and automatically renewed, is genuinely sufficient for the vast majority of websites on the internet.
The edge cases, things like EV certificates, custom certificate authorities, and complex multi-domain configurations, matter for large enterprises with specific compliance requirements. They don’t matter for your blog or small business site. Spending hours researching those topics when you could spend 20 minutes setting up Certbot is a poor trade.
Focus on the fundamentals. Get SSL installed, get auto-renewal working, enable HSTS, and run an SSL Labs test. That’s the whole job for most sites.
Secure your website with confidence
SSL doesn’t have to be intimidating. As you’ve seen, the right certificate, combined with automation and a few simple best practices, gives your website the security and credibility it needs without ongoing headaches. The hardest part is usually just getting started. Choosing a hosting provider that handles SSL setup and renewal for you makes that first step much easier. At DigiHost Guide, we’ve reviewed and compared top web hosting providers specifically to help you find options that include seamless SSL support, free certificates, and one-click HTTPS activation. Take a look and find a host that handles the technical side so you can focus on building your site.
Frequently asked questions
Is an SSL certificate necessary for all websites?
Yes, SSL certificates are important for every website to protect visitors and meet browser security standards. 10.94 billion certificates were issued in Q1 2026, showing SSL is now the universal standard across the web.
Does SSL slow down my website?
No, modern stacks (TLS 1.3 + ECDSA) add less than 5% overhead and can actually optimize your Core Web Vitals scores, supporting better SEO performance.
What happens if my SSL certificate expires?
Visitors will see a security warning and most will leave immediately. Expiration is the most common failure, so always automate renewal at least 30 days before the expiration date.
Which SSL certificate type should I choose as a beginner?
A Domain Validated (DV) certificate is the easiest to set up and sufficient for most websites. 96.8% of SSL certificates are DV, confirming it’s the practical choice for the vast majority of site owners.
How can I automate SSL certificate renewal?
Use Certbot, cert-manager, or your hosting provider’s built-in tools to handle renewal automatically. Automating ACME renewal with these tools and monitoring expiry dates eliminates the most common SSL failure point entirely.
Recommended
- 10 Essential Website Security Features from your Webhost Company
- How Web Hosting Works: A Complete Beginner’s Guide
